Senior Editor: Alan Agbele
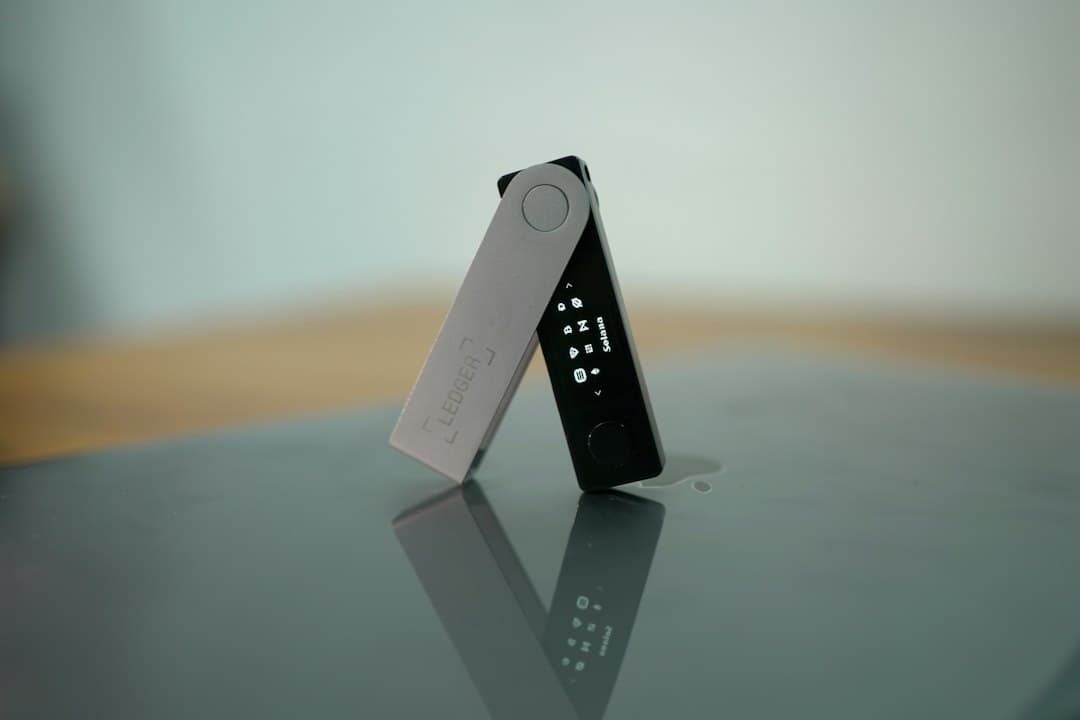
Ledger has confirmed that a spy chip implanted during the manufacturing process was behind a series of cryptocurrency thefts affecting its hardware wallet users. The disclosure marks one of the most significant supply chain compromises in the consumer crypto hardware sector to date, and it shifts the threat model for every device that claims to keep private keys offline.
How the Ledger Supply Chain Compromise Unfolded
The attack vector centers on the period between component production and final delivery. According to Ledger, a spy chip was implanted into devices at some point in the supply chain, allowing attackers to intercept or extract sensitive data from wallets. The company has not disclosed the exact number of affected devices or the specific manufacturing partners involved.
This is not the first time Ledger has faced scrutiny over its supply chain. In 2020, the company suffered a data breach that exposed customer email addresses and home addresses, leading to phishing attacks and even physical threats against users. That incident was a data leak, however, not a hardware compromise. The current disclosure represents a more direct threat because it targets the physical integrity of the device itself.
Why This Matters
The implications extend far beyond Ledger. Every hardware wallet manufacturer relies on a global supply chain that includes chip fabricators, assembly plants and logistics providers. If a spy chip can be implanted in one brand's devices, the same vulnerability likely exists across the industry.
For consumers, the practical consequence is that buying a hardware wallet from a third-party reseller or an unverified marketplace now carries a measurable risk of receiving a compromised device. Ledger users who purchased directly from the company's official store may still be affected, but the attack surface is widest for those who bought through secondary channels.
For the broader crypto market, the incident could accelerate a shift toward verifiable supply chain practices. Expect increased demand for tamper-evident packaging, independent hardware audits and on-device attestation that proves a wallet has not been modified. Competitors such as Trezor and Coldcard may face pressure to demonstrate that their own supply chains are secure, even if they are not implicated in this specific attack.
What You Need to Know About Protecting Your Assets
If you own a Ledger device, the immediate priority is to verify whether your unit was purchased through an authorized channel. Ledger has published guidance on its website for checking device authenticity. Users who suspect tampering should stop using the device and contact the company directly.
More broadly, the incident reinforces a principle that security researchers have repeated for years: hardware wallets are only as trustworthy as the supply chain that delivers them. A device that leaves the factory in a secure state can still be compromised before it reaches your hands.
The Bigger Picture for Hardware Wallet Security
The crypto industry has long treated hardware wallets as the gold standard for self-custody. That assumption rests on the idea that a dedicated device with no network connection is inherently safer than a software wallet on a phone or computer. The Ledger spy chip incident challenges that assumption by showing that the threat can arrive before the device is ever powered on.
Supply chain attacks are not new. Nation-state actors have targeted hardware manufacturers for years, and the 2020 SolarWinds breach demonstrated how a compromised software update could reach thousands of organizations. The Ledger case extends that logic to physical hardware, where the consequences for individual users are immediate and irreversible. Unlike a software patch, a spy chip cannot be fixed with a firmware update.
For Ledger, the reputational stakes are high. The company has built its brand on the promise of secure self-custody. Confirming a hardware-level compromise undermines that promise and could push some users toward competitors or toward alternative custody models such as multi-signature setups that distribute risk across multiple devices.
What Comes Next for Ledger and Its Users
Ledger has not yet announced a recall or a replacement program for affected devices. The company is likely working with its manufacturing partners to identify the point of compromise and to strengthen verification procedures. Users should expect updated guidance in the coming weeks.
The incident also raises a question that the crypto industry has largely avoided: How much do you actually know about the factory that built your hardware wallet? Until that question has a verifiable answer, the promise of offline security will remain incomplete.