Senior Editor: Alan Agbele

Using Sign In With Google has become the default way to log into everything from fitness trackers to tax portals. That convenience, however, creates a single point of failure that most users never audit until it is too late.
The Single Point of Failure Nobody Audits
The core problem is architectural, not incidental. Sign In With Google turns your Google account into a master key for dozens of unrelated services, from productivity tools to retail accounts.
That design is efficient, but it concentrates risk. A password reset on one site is annoying. A compromised Google account can expose every connected service simultaneously.
Security researchers have long warned that users treat single sign-on as a convenience feature rather than a security boundary. The result is a sprawling, undocumented web of dependencies.
How the Lockout Actually Happens
Account lockouts rarely stem from a dramatic hack. More often, they follow a mundane trigger: a forgotten password, a suspicious login flag or a policy suspension.
When Google freezes an account, every third-party service that relies on Sign In With Google can reject the user. Recovery then depends on each site's support process, which varies wildly.
Users who never set a backup email or a secondary login method face the hardest path back. Some services offer no recovery route at all.
Why This Matters
The risk is not theoretical for the millions of people who use Sign In With Google as their only login method. A single account issue can cascade into lost access to email, banking-adjacent services and work tools.
Regulators are also paying closer attention to identity concentration. The same dependency that makes Google convenient makes it a systemic chokepoint for consumer access.
Users who diversify their login methods, and companies that offer fallback authentication, will be better positioned as scrutiny of single sign-on grows.
What Users and Platforms Should Do Next
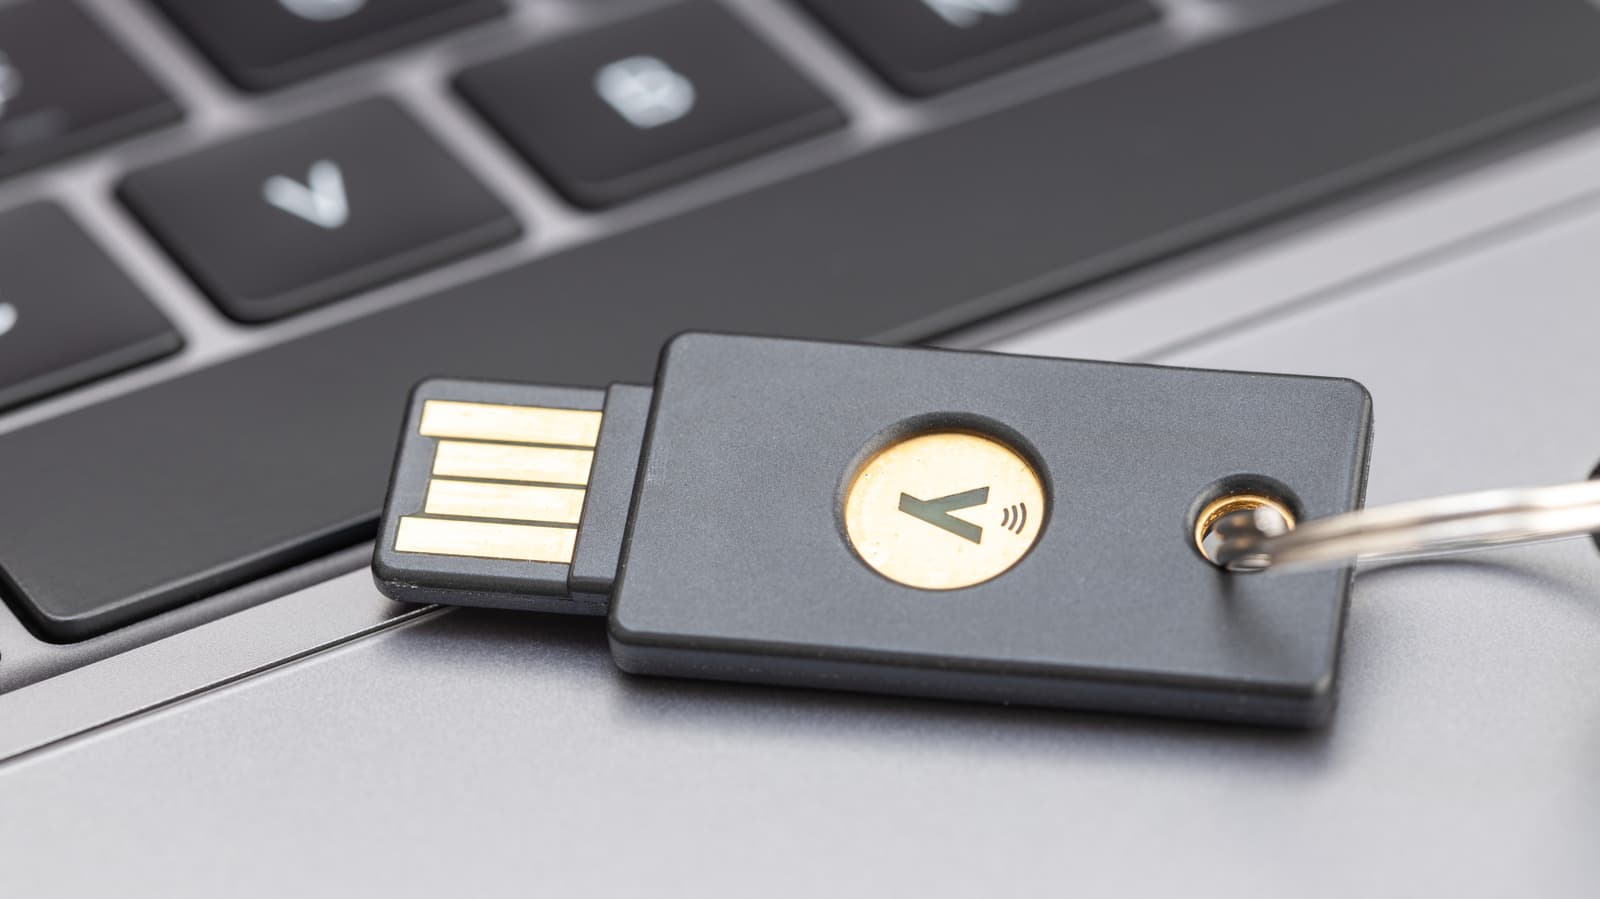
The practical fix is inventory and redundancy. Users should review which services rely on Sign In With Google and add a backup email or password where possible.
Platforms, meanwhile, face pressure to offer alternative login paths. Relying exclusively on Google as an identity provider transfers operational risk from the platform to the user.
That imbalance is likely to draw regulatory attention as digital identity becomes a bigger policy issue. The convenience of Sign In With Google is real, but so is the exposure it creates.