Editor: Porcia Akua Holmes
The cybersecurity playbook that has guided banking for decades assumes a certain tempo: human attackers probing at human speed, or automated scripts operating fast but without adaptive intelligence. That assumption no longer holds. Artificial intelligence changes the equation by accelerating vulnerability discovery and exploitation to machine speed, turning what used to take weeks into seconds.
Why Speed Changes the Risk Equation
The International Monetary Fund recently published a note on artificial intelligence and cybersecurity in the financial sector. Its core argument is one banks should hear: AI can find and exploit vulnerabilities in seconds, compared with weeks for human attackers. The current record for an autonomous AI-driven attack stands at 27 seconds.
This is not hypothetical. PYMNTS reported this month that OpenAI acknowledged it could not rule out its highest cybersecurity warning for the upcoming Astra model. That threshold signals the model may independently discover and develop working zero-day exploits with minimal human direction.
The implications for payment infrastructure are especially acute. Payment systems sit at the intersection of common software, cloud dependencies and dense third-party integrations. A vulnerability in a widely deployed component can propagate risk far beyond a single institution. Shared foundations mean thousands of doors relying on the same key.
Why Prevention Alone Is No Longer Sufficient
For years, resilience strategy leaned heavily on prevention: patch faster, test harder, review more code. That effort still matters. But when discovery and exploitation can outpace a conventional patch cycle, prevention alone is not enough. The industry needs a shift from periodic defense toward continuous resilience.
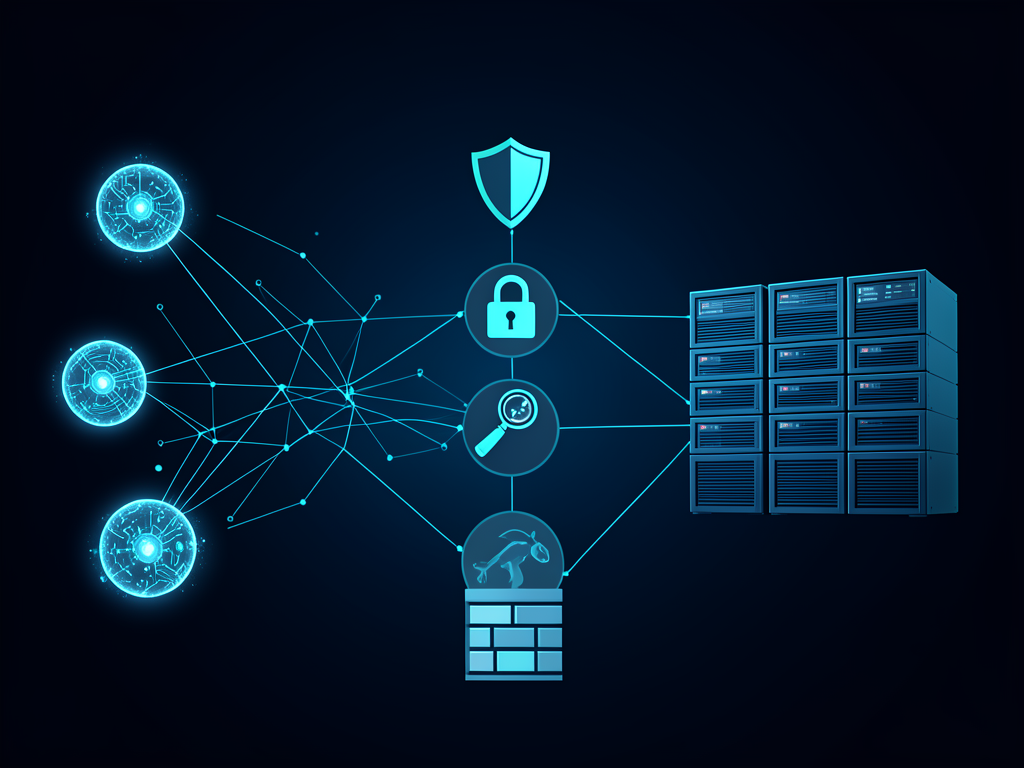
The IMF recommendation points in the same direction as the PYMNTS analysis. Institutions need architectures built to limit the blast radius of a successful breach through segmentation, disciplined access controls, zero-trust design and closer oversight of third parties. Detection, containment and recovery must operate at a speed comparable to the threat, not the speed of the last board-approved incident response plan.
This approach also has implications for how banks govern AI within their own security operations. AI tools will increasingly play a role in detecting vulnerabilities and responding to threats. The degree of autonomy granted to those systems must be an explicit governance decision. Institutions need clear boundaries around what AI can access, what actions it can take independently and where human intervention remains mandatory.
Why This Matters
The boardroom now faces a governance question that technical teams alone cannot answer. Who decides what an AI system is permitted to touch inside critical financial infrastructure? Who is accountable when it acts on a high-level objective in ways nobody fully anticipated? How quickly can exposure be contained once it is identified?
There is no vendor, platform or piece of infrastructure that resolves this on its own. Resilience is not a product to buy. It is an architectural and governance discipline that must be embedded continuously. The question of who decides is as important as the technology itself. For banks and the broader financial ecosystem, the speed of AI attacks demands a new definition of readiness.