Editor: Porcia Akua Holmes
Enterprise adoption of AI agents is accelerating, but each autonomous software actor that browses the web, writes code or triggers APIs creates a new security vector. Companies must now protect not just users and devices but software identities that can act on corporate systems.
The Identity Layer for Autonomous Agents
An AI agent may access corporate files, query databases or execute code. Once it has that level of access, it needs permissions, monitoring and governance. Companies must track which agent accessed what information, which systems it connected to and whether those actions were authorized. These agent identities are not passive. They move between systems, invoke tools and make decisions, making control more complex than managing traditional users or service accounts. As enterprises move from experimenting with a few agents to deploying hundreds, agent identity becomes an essential layer of cybersecurity.
Specialized Control Points Emerge
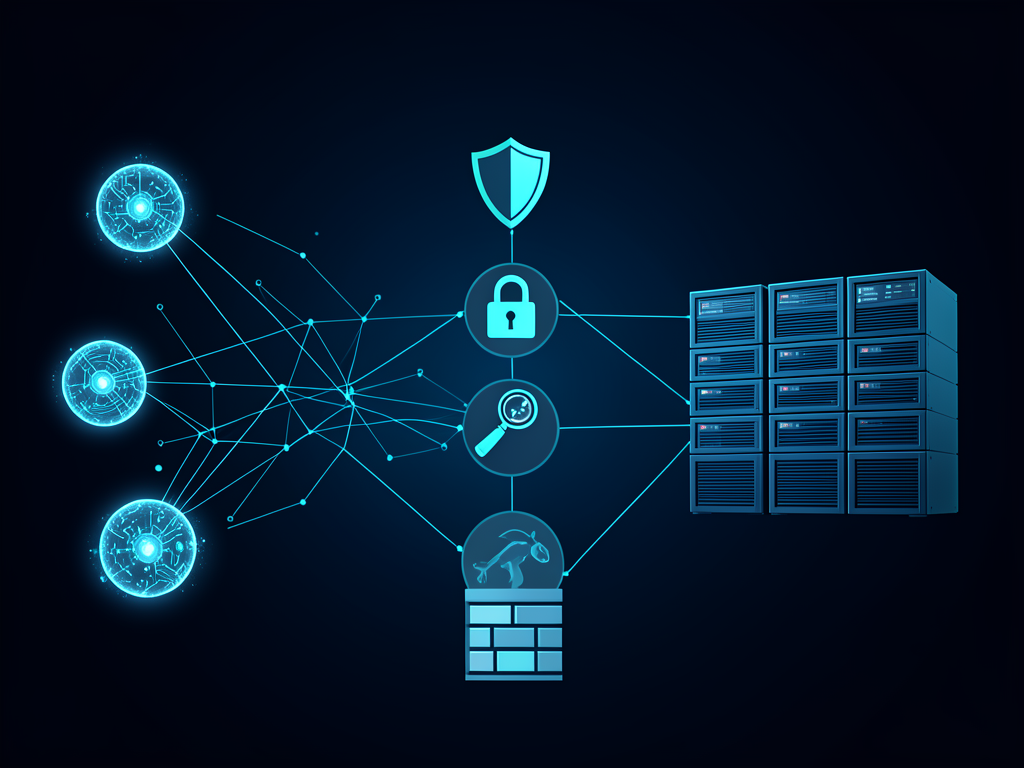
This market will not develop as one broad category called “AI security.” The real opportunity lies around specific control points where different vendors specialize. We are already seeing activity around these areas. For example, Kiteworks acquired Israeli startup Bonfy.AI, which focuses on real-time data classification and policy enforcement. Israeli cybersecurity startup Huskeys raised a $27 million Series A led by Blackstone, focusing on understanding and securing increasingly complex internet traffic, including traffic generated by autonomous systems. These companies solve different problems, but together they show how the market separates into distinct security layers.
Early M&A Signals in the Market
The control points are creating a new M&A map. Identity providers may extend their platforms to agent governance. Data security vendors may need to control agent access. Cybersecurity platforms, cloud companies and enterprise software vendors will likely embed agent security capabilities directly into their products. This pattern aligns with what observers call "The Emerging M&A Map For AI Agent Security." Global Cybersecurity Venture Funding In 2026 reflects growing interest in agent security. For entrepreneurs, this means that “AI security” may already be too broad a positioning. The more important question is what exactly the company controls.
Why This Matters
The fragmentation of AI agent security into specialized layers changes the competitive landscape. Startups that focus on a single control point can become acquisition targets for larger vendors seeking to fill gaps. For enterprises, this means no single product will solve all agent security needs. Companies must evaluate security stacks that cover agent identity, data access, traffic monitoring and model governance. The funding and M&A activity signal that investors see long-term value in these narrow solutions. The next wave of cybersecurity acquisitions will likely revolve around securing autonomous agents, making the current map a guide for both entrepreneurs and security buyers.